 Web DevelopmentWordPress VIP or Self Hosted Enterprise WordPress in the UAEWordPress VIP or self hosted enterprise WordPress in the UAE: compare data residency, hosting SLA, cost drivers and code review rules, plus key setup notes.
Plugin Governance: Keeping WordPress Lean as It Grows
WordPress plugin management for growing sites: an approval policy, a plugin register, update rules and a quarterly audit that keep many editors on a lean site.
WordPress plugin management at scale needs a written policy, not good intentions. Decide who can request a plugin, what it must pass before installation, who owns it once it is live, and when it is reviewed again. With that in place, a site with many editors and contributors can keep adding features without slowly turning heavy, fragile and hard to update.
Why plugin sprawl happens on growing sites
Few sites end up with too many plugins through one bad decision. It happens one reasonable request at a time. A marketing manager needs a popup for a campaign. A developer adds a helper for a single page. An agency installs a form tool, then a second one for a different team. The campaign ends, the developer moves on, and the plugins stay.
The cost shows up in three places:
- WordPress performance. Many plugins load scripts and styles on every page, whether or not that page uses them, and some add database queries to each request.
- Security exposure. Every plugin is code from a third party running with access to your site. An abandoned plugin with a known vulnerability is a common entry point.
- Update risk. The more plugins interact, the more likely it is that one update breaks something else, which makes teams nervous about updating at all.
The answer is not a hard cap on the number of plugins. One well maintained plugin that replaces three overlapping ones is a gain. The answer is a plugin approval policy that treats every addition as a decision someone owns.
A plugin approval policy for WordPress plugin management
The policy below suits organisations where several people can ask for changes: a marketing team, product owners, regional editors and one or more development partners. Adjust the roles to your own structure.
Step 1: requests go through one channel
Nobody installs a plugin directly on the live site. Requests are raised in one place, such as a ticket queue or a shared form, and describe the business need rather than a specific product. "We need event registration with payment" is a better request than "please install plugin X", because it allows the reviewer to consider options, including features the site already has.
Step 2: check whether a plugin is needed at all
Before evaluating any product, the reviewer asks:
- Can WordPress core or the current theme already do this?
- Does an installed plugin already cover it?
- Is the need permanent or tied to a short campaign?
- Would a small piece of custom code in the theme be simpler and lighter?
Step 3: evaluate the candidate
| Criterion | What to look for |
|---|---|
| Maintenance | Recent updates, compatibility with the current WordPress version, and an active support channel |
| Track record | Publicly reported vulnerabilities and how quickly the developer fixed them |
| Footprint | Whether scripts and styles load site wide or only where the feature is used |
| Data handling | What personal data it stores or sends to outside services, and where |
| Licence and vendor | Who holds the licence, when it renews and whether the company account owns it |
| Exit route | What happens to content or shortcodes if the plugin is later removed |
The data handling question matters in the UAE, where forms, chat tools and analytics plugins may process personal data covered by the UAE Personal Data Protection Law or, for businesses in DIFC or ADGM, their own data protection regimes. Confirm which rules apply with your legal adviser or the relevant regulator.
Step 4: test on staging, then approve
The plugin is installed on a staging copy first. The reviewer checks key templates, forms and checkout flows, compares page weight and loading behaviour before and after, and confirms that nothing else breaks. Only then does a named approver sign it off. Our guide to staging, QA and rollback for WordPress releases covers this process in more detail.
Step 5: record it in the plugin register
Every approved plugin gets an entry in a simple register, kept in a shared spreadsheet or your ticketing tool.
What the plugin register should hold
- Plugin name, purpose and the business need it serves
- Business owner (who asked for it) and technical owner (who maintains it)
- Date approved and date of last review
- Licence holder and renewal date, for paid plugins
- Pages or features that depend on it
- Whether auto updates are enabled, and why
- Notes on data it collects or shares
The register turns plugin management from memory into evidence. When someone asks why a plugin is there, the answer takes seconds to find.
Roles and permissions that make the policy stick
A policy only works if the platform enforces it. In most organisations, only a small number of administrators should be able to install, activate or update plugins. Editors and authors should not see those controls at all.
- Keep administrator accounts to named individuals, with two factor authentication.
- Disable plugin and theme file editing from the dashboard, as the WordPress hardening guide recommends.
- Give development partners their own named accounts so changes can be traced.
For a fuller treatment of roles and approval chains, see WordPress admin governance: roles, approvals and MFA.
Updates: automatic or controlled?
Since WordPress 5.5, administrators can switch on automatic updates plugin by plugin and theme by theme, according to the WordPress documentation on auto updates. That flexibility is useful, but it needs a rule.
A practical split
- Automatic updates for small, low risk plugins that do not affect layout, forms or payments, provided backups run daily and someone watches the update notification emails.
- Controlled updates through staging for plugins that power checkout, forms, multilingual content, membership or page building, where a faulty update could stop the business.
- Security releases applied quickly, even outside the normal cycle, once they have passed a short staging check.
The quarterly plugin audit
Approvals stop new problems. A quarterly plugin audit removes the old ones. Block a few hours each quarter and work through these steps.
- Compare the register with reality. List every installed plugin, active and inactive. Anything not in the register is either added with an owner or scheduled for removal.
- Delete inactive plugins. Deactivated plugins still sit on the server. If nobody needs them, remove them completely.
- Check maintenance status. Flag any plugin that has not been updated in a long time, has been closed in the WordPress plugin directory, or lacks support for the current WordPress version.
- Look for overlap. Two form plugins, two SEO tools or three slider plugins are common findings. Consolidate onto one.
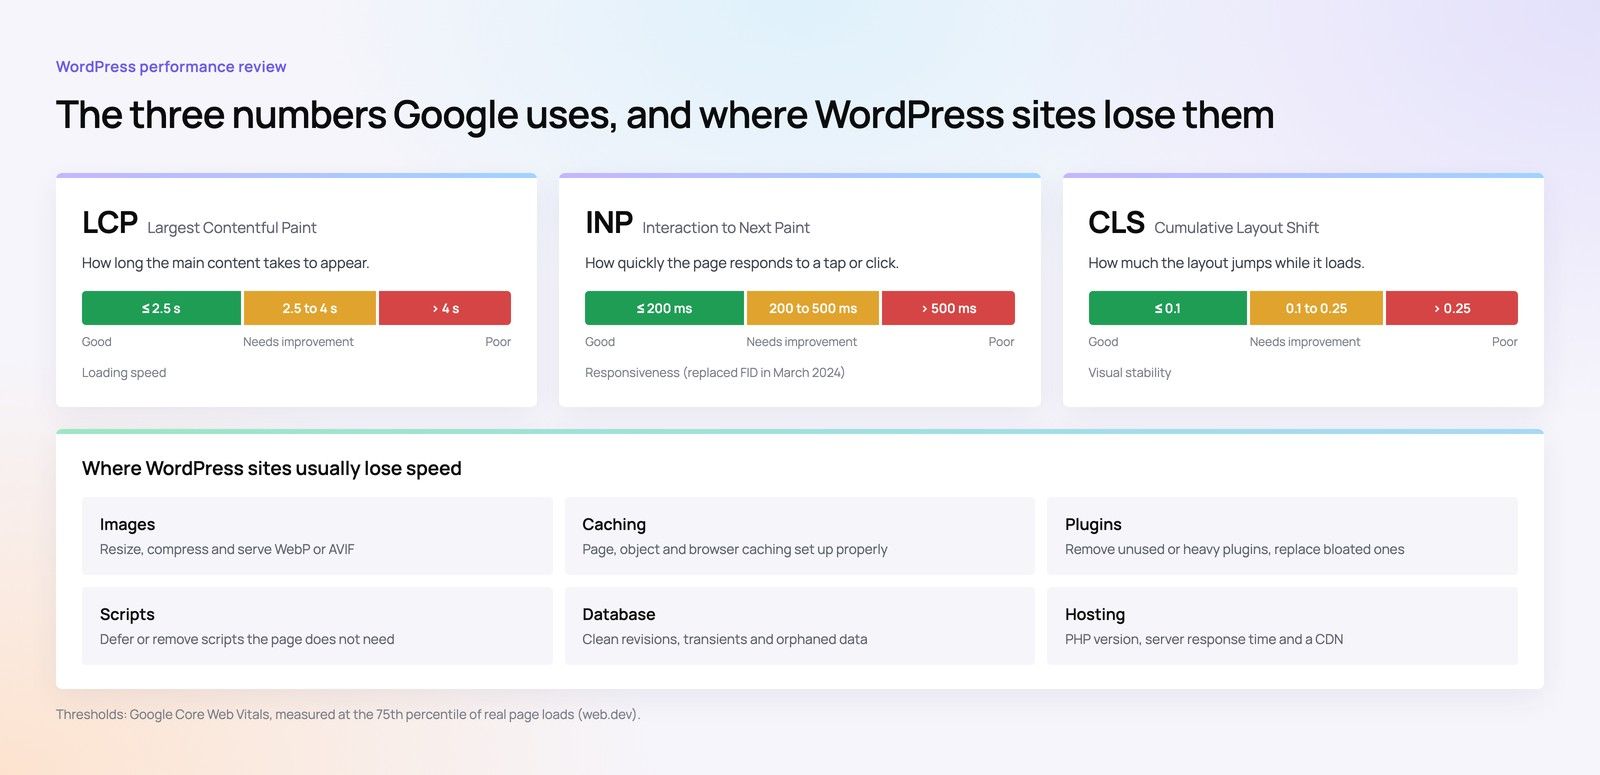
- Measure the cost. Use a staging copy to see which plugins add the most scripts, styles and queries to key pages.
- Confirm ownership. If a business owner has left, assign a new one or retire the plugin.
- Review licences. Check renewals and make sure licences are held by company accounts, not personal ones.
Hypothetical example: a regional retailer's site has 46 active plugins after four years and several agencies. The first audit finds two form plugins, three tools that each add tracking scripts, and a slider used on one retired campaign page. Consolidating and removing them shortens the plugin list substantially, and the team agrees that any new request now goes through the register.
Signs your site has too many plugins
- Updates are postponed because nobody is sure what they will break.
- Pages that look simple are heavy, with many separate script and style files.
- Nobody can explain why certain plugins are installed.
- Different teams use different tools for the same job.
- Site Health in the WordPress dashboard repeatedly reports inactive plugins or outdated components.
If several of these apply, start with the audit rather than the policy. Clean up first, then put the approval process in place so the site stays lean. Our look at why WordPress still earns its place explains why disciplined maintenance is what keeps it a sound choice, and headless or traditional WordPress covers architectures where front end plugins matter less.
Get help bringing your plugins under control
Codeeo's WordPress development team can run a plugin audit, consolidate overlapping tools, replace fragile plugins with lighter custom code where it makes sense, and set up the register and approval process with your team. If speed is the main concern, our speed optimisation quick start is a focused place to begin. We have delivered 200+ projects across the UAE and the US, and UAE clients can meet the team at our Dubai office. Contact us to discuss your site.
Frequently asked questions
No single number applies.
A site with forty well built, focused plugins can be faster than one with ten heavy ones. What matters is what each plugin loads, how well it is maintained and whether it overlaps with others. Measure the effect of each plugin on key pages rather than counting them, and remove anything that does not earn its place.
Web DevelopmentWordPress VIP or Self Hosted Enterprise WordPress in the UAEWordPress VIP or self hosted enterprise WordPress in the UAE: compare data residency, hosting SLA, cost drivers and code review rules, plus key setup notes. Web DevelopmentWhat a WordPress Maintenance SLA Should CoverWhat WordPress maintenance services should cover in writing: core and plugin updates, security, backups, multilingual publishing support and response times.
 Web DevelopmentWordPress Release Management: Staging, QA and RollbackA WordPress deployment workflow that releases safely: Git based builds, a staging site that mirrors live, smoke tests to run and a rollback plan written first.
Tell us what the business needs. We will tell you what to build first.
Schedule a free consultation and get a written recommendation, with costs, before you commit to anything.
Get in touchPROVEN RESULTS
4.7 / 5verified reviews on Google